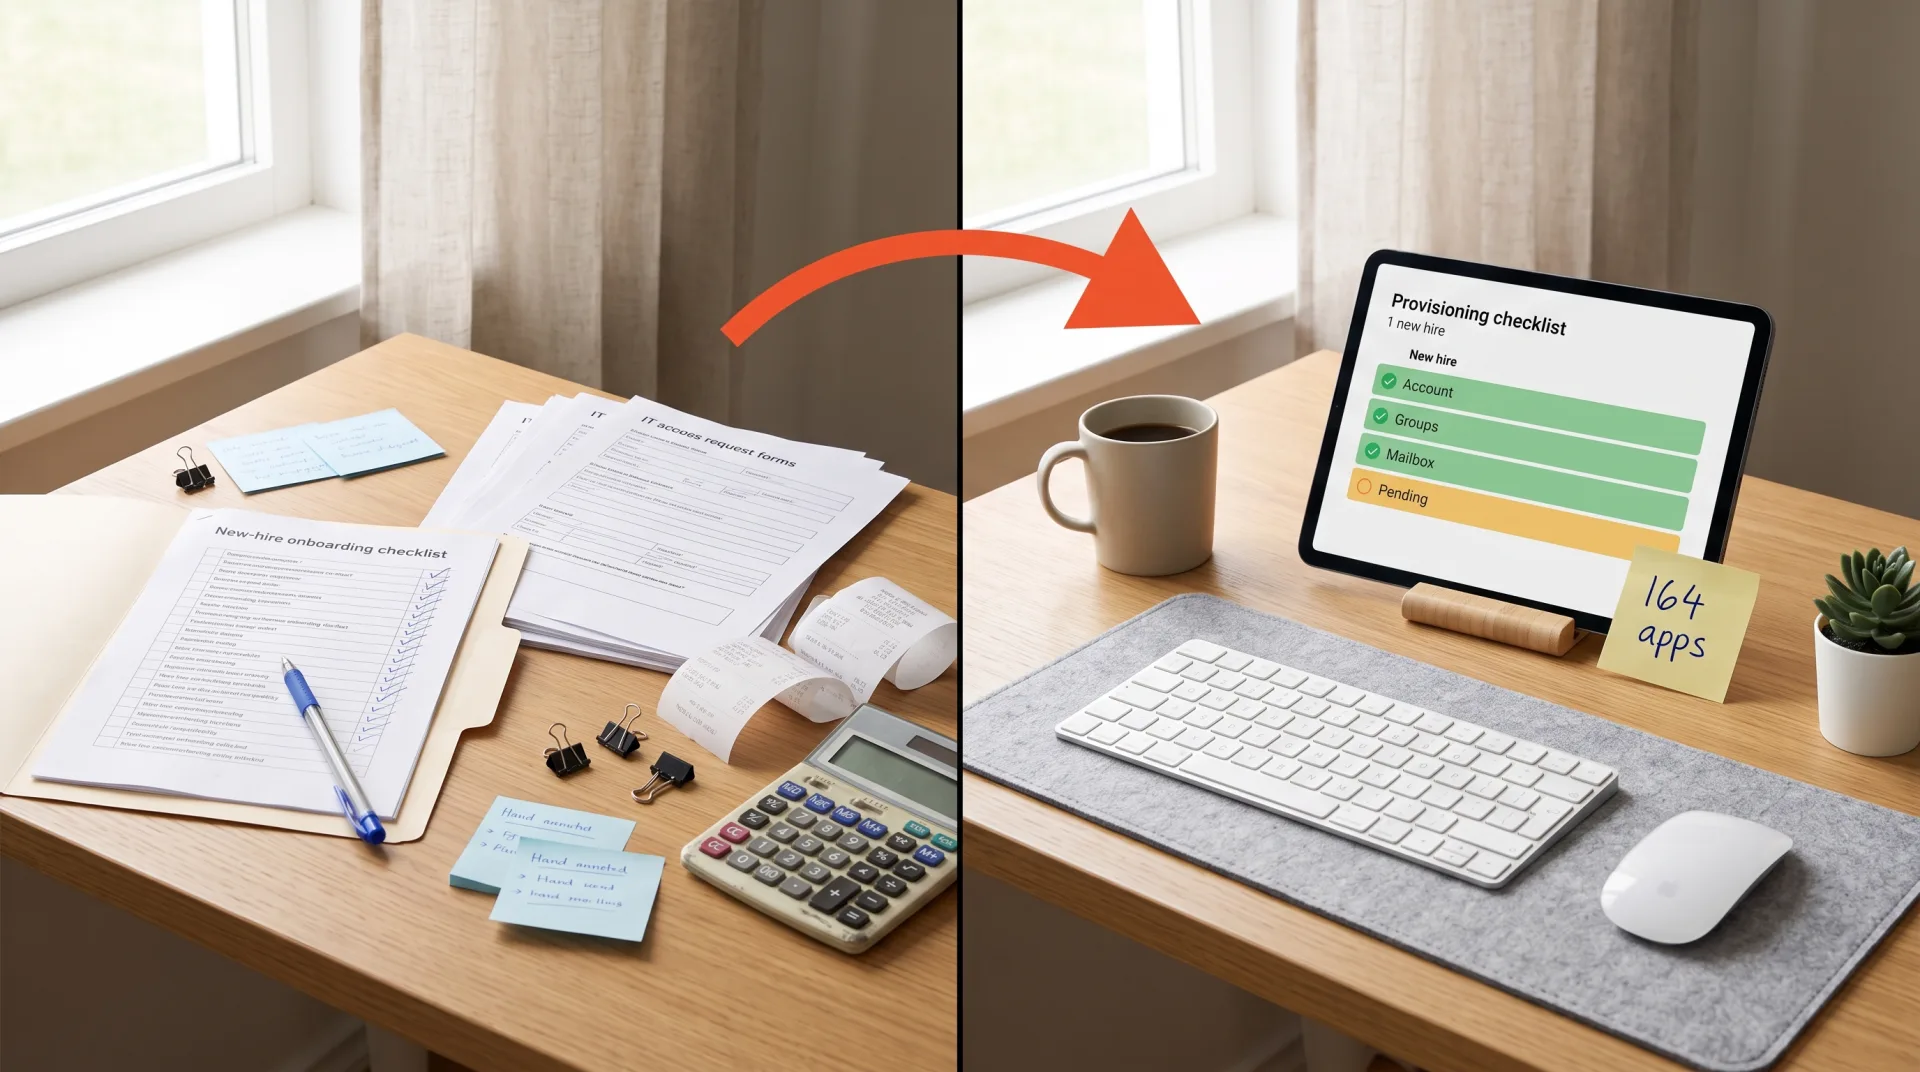
In BetterCloud's mid-market sample, the average app count went from 116 to 164 in a single year, a 41% jump (BetterCloud, 2026, n=525 IT and security professionals). Okta's cross-customer average, published in March 2025, was 101 apps (Okta, 2025). Take either number and the job has the same shape: every app is a door, and a new hire needs some subset opened on day one and all of them closed on their last.
Most guides to employee onboarding automation assume you already run an HRIS as the system of record and only need to connect it. Companies of 20 to 200 people usually do not. The handoff spans HR or the founder, IT, finance, the hiring manager and whoever orders the hardware, and the person who knows the start date is rarely in a system that can tell another system about it. The problem is not a missing integration. It is a missing event.
This is a spoke in Lane 01, automating your daily ops, and it links up to our Ops Automation Playbook, the pillar ranking which workflows are worth attacking first.
By Dan Colta. We are a founder-led EU automation studio building owned automations for SME teams. Wiring up joiners and leavers is one of the jobs those builds keep running into. This guide comes out of that work rather than a vendor template.
Key Takeaways
- In BetterCloud's mid-market sample, average app counts rose 41% in one year, from 116 to 164, so every hire and every exit touches more doors than the last one did (BetterCloud, 2026).
- You do not need an HRIS. You need one roster of record and one upstream system that can emit a machine-readable event. The earliest one is usually the e-signature webhook on the offer, not the HR tool.
- Offboarding is where the failure is countable: USAID missed its own 24-hour disable requirement on its travel system for 76% of separated users (137 of 178), with 33 accounts having no record of ever being disabled (USAID OIG, 2025).
- In the past 12 months, 18% of organizations reported a breach caused by an offboarded user who still had access (BetterCloud, 2026). The median breach impact is roughly $38,000 for an SMB under $25M in revenue, which is where most 20 to 200 person companies sit, not the enterprise headline figure (Verizon, 2026).
- The like-for-like buy option is the lifecycle add-on, not the identity license: Microsoft Entra ID Governance at $7.00 per user per month on top of Entra ID P1 at $7.00, or Okta Workforce Identity Essentials with Lifecycle Management at $17. Rippling publishes no per-user price at all.
Why does onboarding automation break at 20 to 200 people?
Because the handoff has several owners and no system of record. At that size HR is often the founder, IT is a contractor or whichever engineer is most patient, and finance is an external accountant. BetterCloud's 2026 survey found 62% of IT leaders say manual work is actively preventing them from doing strategic projects (BetterCloud, 2026, n=525).
Below 20 people the manual version works, because hires are rare enough that one person holds the sequence in their head. Above 200 you have bought an HRIS and the vendor guides apply. The band in between is where hiring frequency has passed what memory handles, while budget has not passed what a platform costs.
There is also a sunk cost behind every one of those first weeks. By the time someone starts you have already paid to find them, and a first week with a late laptop is a bad way to spend that. If the pipeline upstream is also manual, the candidate routing agent build covers that stage.
What does the handoff actually look like?
It is about seven steps across five owners, and only two sit in a system that can emit an event on its own. Everything else is a human remembering. Zylo's 2026 SaaS Management Index, built on over 40 million licenses, found organizations leave 36% of their SaaS licenses unused (Zylo, 2026), and unreclaimed seats from leavers are one contributor.
Draw the map by which step can tell another system that something happened, not by department:
| Step | Owner | Can it emit an event? | Practical trigger |
|---|---|---|---|
| Offer signed | Hiring manager or founder | Usually yes | E-signature completion webhook (DocuSign, Dropbox Sign) |
| Contract and payroll setup | Finance or external accountant | Rarely | Manual confirmation, or a scheduled export |
| Identity created | IT | No, it is an effect | API call to Google Admin SDK or Microsoft Graph |
| App access granted | IT or app owner | Partially | Group membership in the identity provider, SCIM where supported |
| Hardware ordered | Office manager or IT | No | Dated checklist task with a named owner |
| Day-one schedule | Hiring manager | Yes | Calendar API, invites generated from a template |
| Leave date known | Manager, sometimes only verbally | Almost never | The event nobody owns |
Read the third column and the design falls out. The offer signature is often the only machine-readable moment, and the leave date, the security-critical one, has no emitter at all.
One observation from our own builds, and it is one shop's experience, so weight it accordingly: the event that survives is rarely the one the client names first. Teams point at the HR tool when we ask what should fire the handoff, then that tool turns out to have no outbound webhook, and the earliest machine-readable moment is the e-signature on the offer. We now open scoping by asking which systems can emit rather than which hold the record, and the answer reorders the build.
Which parts can you automate without an HRIS?
Everything downstream of a single roster row. The requirement is not an HRIS, it is one table holding the person, the start date and the leave date, plus one upstream system that can emit a machine-readable event. Okta measured 101 apps per company in March 2025 (Okta, 2025), and you do not need to integrate all of them.
Pick the roster deliberately: dates live in exactly one place. An Airtable base, a Postgres table or a Google Sheet all work. What matters is that nothing else is allowed to be the authority on when someone starts or leaves, because once two systems both hold a leave date, one will be wrong and that is the one your automation reads.
Sort the app estate into three tiers, because they automate differently.
Tier 1, SCIM-provisioned. The app supports SCIM against your identity provider, so adding a person to a group creates their account and removing them deactivates it. Google Workspace and Microsoft Entra both act as the source. Automatic in both directions, so push as much of the estate here as you can.
Tier 2, API-provisioned. No SCIM, but a REST API with create-user and deactivate-user calls. Two functions per app, called from the same sequence. Most mid-size SaaS lands here.
Tier 3, manual. Small vendors, regional tools, anything where a seat is bought by emailing a person. Automate the reminder instead: the task appears with an owner and a due date, and the sequence does not close until someone marks it done.
Trying to make tier 3 disappear is the mistake. Make it visible and dated instead. The buy-or-build call that tiering forces is the one mapped in workflow automation examples.
How do you build the provisioning checklist?
As a table with an owner, a system, an action, a due offset and an idempotency key, not as a document. It must be safely re-runnable, because it will be re-run. Okta's Businesses at Work 2026 reported the average number of access requests per company more than doubled in a year, up 1140% over two years (Okta, 2026, platform data November 2024 to October 2025).
The sequence itself is short. On the trigger event, with the start date read from the roster:
- Create the identity using a deterministic username rule, so the same person always resolves to the same address.
- Add them to groups derived from role plus team. Groups, never individual grants, because groups are what you remove later.
- Let SCIM provision tier 1 apps off that group membership.
- Call the tier 2 create-user APIs.
- Create the mailbox, aliases and calendar, then send day-one invites from a template.
- File the hardware order with a due date before the start date, not on it.
- Open the payroll and contract task for finance, roster row attached.
- Post the checklist state into the channel the hiring manager already works in.
Idempotency is the part people skip and then regret. Key every task on the pair of person ID and task ID, and record completion before treating the sequence as advanced. Prefer create-if-absent semantics: Google's Directory API and Microsoft Graph both return a conflict when a primary address already exists, and your handler should treat that as success rather than an error worth retrying. A job you cannot safely re-run is a job you will be afraid to touch.
Keep exactly one manual gate, and put it on the grant. Before any account is created or any paid seat is bought, a human confirms the start date is real. Offers get rescinded and start dates slip far more often than the automation fails, and every premature grant is a line on an invoice nobody tracks. An Approve button in the channel the team already reads is enough, the same pattern as ops from a single Slack channel.
Notice the asymmetry, because it decides the offboarding design too. The grant gets a human gate. The revoke does not.
Offboarding is the half most teams skip
Offboarding is the mirror of onboarding, and it is the half where failure is measurable. A USAID Office of Inspector General audit published on 13 May 2025 found the agency did not disable travel system accounts for 76% of users, 137 of 178, within 24 hours of their separation as its own ADS 545 policy required (USAID OIG, 2025).
Dormant accounts would be one thing. These were not. The same audit found almost 57% of one sampled group, 19 of 33 users, accessed the travel system after their separation date, eight of them more than 325 days after leaving (USAID OIG, 2025). That is a federal agency with a written policy and an audit function. A 40-person company whose leave dates live in a manager's head is not doing better.
Two triggers cover the whole problem, and neither needs an HRIS. A nightly job reads leave dates from the roster and fires at midnight on the last day, which handles resignations. A manual revoke command, one button in the ops channel, handles the rest. Then the order matters more than the speed.
| Order | Action | Why it sits here |
|---|---|---|
| 1 | Revoke active sessions and refresh tokens at the identity provider | Disabling an account does not always terminate a live session |
| 2 | Disable the identity, do not delete it | Deletion destroys the audit trail and orphans file ownership |
| 3 | Reset the password and remove MFA factors | Blocks re-enrollment from a device still in their hand |
| 4 | Remove from every group | Group membership grants app access, so this cascades |
| 5 | Transfer file and calendar ownership | Google and Microsoft both orphan documents owned by deleted users |
| 6 | Forward or delegate the mailbox to the manager | Keeps customer threads alive without the account |
| 7 | Reclaim paid seats in tier 2 and tier 3 apps | The invoice keeps running until somebody removes the seat |
| 8 | Revoke API keys, personal access tokens and shared credentials | These survive account disablement entirely |
Step 8 is the one most builds miss. A personal access token on a repository, an API key in a CI pipeline, a shared credential in a vault: none die when the account is disabled, and none appear in the identity provider's list of what that person had. If you build one thing from this section, build that inventory.
BetterCloud's 2026 survey found 18% of organizations experienced a data breach caused by an offboarded user who still had access (BetterCloud, 2026, n=525), and Verizon's 2026 DBIR executive summary put credential abuse at 13% of initial access vectors in SMB breaches (Verizon, 2026).
IBM's Cost of a Data Breach Report 2026 put the average cost of a breach initiated by valid account abuse at USD 5.07 million (IBM, 2026), and it is the figure most widely quoted. That is an enterprise average, not your expected cost. The figure sized to your company comes from Verizon's 2026 Breach Impact Study, built on 38,181 cyber insurance claims with recorded losses between January 2019 and October 2025.
And it is not a fast failure. IBM measured the valid-account breach lifecycle at 179 days to identify plus 64 to contain, 243 days total (IBM, 2026). An orphaned account is a slow leak, which is why nobody notices it until an auditor or an attacker does.
What does it cost to buy this versus build it?
The like-for-like purchase is the lifecycle add-on, not the identity license, and that distinction is where most build-versus-buy comparisons go wrong. Microsoft Entra ID Governance lists at $7.00 per user per month paid yearly, and it sits on top of Entra ID P1 at $7.00, so $14.00 all in (Microsoft, fetched 4 September 2026).
| Vendor and SKU | Public list price | What it actually covers |
|---|---|---|
| Okta Workforce Identity Starter | $6 per user/month | Entry identity tier |
| Microsoft Entra ID P1 | $7.00 per user/month, paid yearly | Identity baseline, no lifecycle workflows |
| Microsoft Entra ID Governance (add-on) | $7.00 per user/month, paid yearly | Lifecycle workflows and access reviews, the like-for-like SKU |
| BambooHR Core | $10 per employee/month | HR record, or a flat rate starting at $250/month at 25 employees or fewer |
| Okta Workforce Identity Core Essentials | $14 per user/month | Identity, still without Lifecycle Management |
| Okta Workforce Identity Essentials | $17 per user/month | Includes Lifecycle Management, plus a $1,500 annual contract minimum |
| BambooHR Pro | $17 per employee/month | HR record with added modules |
| Rippling | No public per-user price | Quote only |
Prices fetched from vendor pricing pages on 4 September 2026: Okta, Microsoft, BambooHR, Rippling.
Run it at 60 people, the middle of the band. Entra ID P1 plus Governance is 60 seats times $14 times 12 months, or $10,080 a year. Okta Workforce Identity Essentials is 60 times $17 times 12, or $12,240 a year. Both scale with headcount.
We are not quoting a build price here, because it depends on how many tier 2 and tier 3 apps you have, and no honest number covers both a 12-app estate and a 90-app one. The shape is what matters. Buying is a per-seat line every month for as long as you employ the person. Building is a one-time scope plus a small always-on server and the maintenance to keep it firing, which does not move when you hire ten more people.
For the manual baseline, here is arithmetic instead of a made-up per-hire admin figure. The US Bureau of Labor Statistics puts the median wage for human resources specialists at $75,940 a year (BLS, May 2025) and computer support specialists at $30.24 an hour (BLS, May 2025). At 2,080 hours the HR figure is about $36.51 an hour, so assuming three hours of HR time and three of IT per joiner-and-leaver cycle, that is about $200 per person in bare salary. The three-and-three is an assumption, the arithmetic is ours on BLS medians rather than a researched finding, and BLS is US data, so substitute your own rates.
That Rippling absence in the table is itself a data point, because you cannot model a line item you cannot see. For where a no-code tool sits between building and buying, see Zapier vs n8n vs Make vs custom code.
When should you just buy the platform?
Buy when you already sit inside one vendor's identity stack, when you need audit artifacts you would otherwise build yourself, or when nobody will own the code. For a company standardized on Microsoft 365, Entra ID Governance at $14 per user per month all in arrives with access reviews attached (Microsoft).
Four honest buy signals:
- Your apps already speak SCIM to your identity provider. The work is configuration, not code, and buying gets you there in a week.
- You need attestation and access-review evidence for SOC 2, ISO 27001 or a customer security questionnaire. Buying gives you the report; building means building the report too, which is more work than the provisioning.
- Headcount is heading past 200, or you are multi-entity. An HRIS earns its keep on payroll and employment compliance alone, and provisioning is the bonus.
- Nobody will maintain it. A provisioning job that silently stops firing is worse than a manual checklist, because people stop checking what they believe is automatic.
The build signals are the mirror image: an estate of small regional vendors with no SCIM, joiners who are contractors and never enter the HR platform, or a per-seat tool you would still pay for alongside the platform.
Most teams in the 20 to 200 band land in between. They buy identity and build the glue: the provider handles tiers 1 and 2, while a small scheduled service handles the roster, the tier 3 reminders and the offboarding sequence. That hybrid is not a failure to decide, and the same job can emit the weekly access summary described in automated weekly reporting.
FAQ
The six questions we get most often about employee onboarding automation are answered in the schema above: what it is, whether it works without an HRIS, what belongs on the checklist, why offboarding is the more urgent half, what the lifecycle SKUs cost, and how fast deprovisioning has to happen.
The bottom line
Stop looking for the integration and start looking for the event. One roster holds the start date and the leave date. One upstream system, often the e-signature webhook rather than the HR tool, tells the roster something changed. Everything else reads from there: groups drive app access, SCIM drives tier 1, two functions per app drive tier 2, and tier 3 becomes a dated task with a name on it.
Then build the offboarding half, because that is where the failure is countable. USAID missed its 24-hour disable requirement for 76% of separated users and had no disable record at all for 33 accounts, and 18% of organizations have already had a breach from an offboarded user who kept access. The asymmetry is the rule: put the human gate on the grant, never on the revoke. Restoring an account takes minutes. A breach that starts with a valid account runs 179 days before anyone identifies it.
If you want a second read on which parts of your handoff can emit an event, or a scoped estimate for building the sequence once instead of renting it per seat, our team can help. Start with the Ops Automation Playbook for the full ranking of which ops workflows to automate first.
Sources (retrieved 2026-09-04):
- USAID Office of Inspector General, Weaknesses in USAID's Management of Travel System Account Closures (Report No. A-000-25-002-M), 13 May 2025: https://oig.usaid.gov/sites/default/files/2025-05/Weaknesses%20in%20USAID%27s%20Management%20of%20Travel%20System%20Account%20Closures%20Highlight%20Concerns%20About%20Protecting%20Travelers%20and%20Sensitive%20Information%20%28Report%20No.%20A-000-25-002-M%29_0.pdf
- BetterCloud, The 2026 State of SaaS report (n=525): https://www.bettercloud.com/monitor/the-2026-state-of-saas-report/
- Verizon Business and CyberAcuView, 2026 Breach Impact Study: https://www.verizon.com/business/resources/reports/2026-breach-impact-study-dbir.pdf
- Verizon Business, 2026 DBIR Executive Summary: https://www.verizon.com/business/resources/executivebriefs/2026-dbir-executive-summary.pdf
- IBM Security, Cost of a Data Breach Report 2026: https://www.ibm.com/reports/data-breach
- Okta, Businesses at Work 2025: https://www.okta.com/newsroom/articles/businesses-at-work-2025/
- Okta, Businesses at Work 2026: https://www.okta.com/newsroom/articles/businesses-at-work-2026/
- Zylo, 2026 SaaS Management Index: https://zylo.com/news/2026-saas-management-index
- U.S. Bureau of Labor Statistics, Occupational Outlook Handbook, Human Resources Specialists (May 2025 wages): https://www.bls.gov/ooh/business-and-financial/human-resources-specialists.htm
- U.S. Bureau of Labor Statistics, Occupational Outlook Handbook, Computer Support Specialists (May 2025 wages): https://www.bls.gov/ooh/computer-and-information-technology/computer-support-specialists.htm
- Okta pricing: https://www.okta.com/pricing/
- Microsoft Entra pricing: https://www.microsoft.com/en-us/security/business/microsoft-entra-pricing
- BambooHR pricing: https://www.bamboohr.com/pricing
- Rippling pricing: https://www.rippling.com/pricing
Frequently asked questions
What is employee onboarding automation?
Employee onboarding automation turns the handoff between HR, IT, finance and the hiring manager into a triggered sequence instead of a chain of reminders. One event, usually a signed offer or a start date written into a shared roster, fires a fixed set of tasks: identity creation, group membership, app access, hardware, payroll and a day-one calendar. It matters because the surface keeps growing. BetterCloud's 2026 State of SaaS report, a survey of 525 IT and security professionals, found mid-market organizations went from an average of 116 apps to 164 in a single year, a 41% jump.
Can you automate onboarding without an HRIS?
Yes, and most companies of 20 to 200 people have to. The requirement is not a human resources information system, it is one roster that everything else reads from, plus one upstream system that can emit a machine-readable event. In practice the earliest reliable trigger is often the e-signature completion webhook on the offer rather than the HR tool. From there the identity provider does the work: Google Workspace Admin SDK and Microsoft Graph both create accounts and group memberships over API, and group membership drives app access wherever SCIM is supported.
What should an automated provisioning checklist include?
A provisioning checklist should be a data structure, not a document. Each row needs an owner, a system, an action, a due offset from the start date, and an idempotency key so re-running the job never creates a duplicate account. Typical rows: identity account, group memberships, mailbox and aliases, app seats, hardware order, payroll record and the day-one calendar. Keep exactly one manual gate, on the grant: a human confirms the start date is real before any account is created or any paid seat is bought, because offers get rescinded and start dates slip more often than the automation fails.
Why is offboarding automation more urgent than onboarding automation?
Because offboarding failures are measurable and expensive, while onboarding failures are mostly embarrassing. A USAID Office of Inspector General audit published on 13 May 2025 found the agency did not disable travel system accounts for 76% of separated users, 137 of 178, within the 24 hours its own ADS 545 policy required. Seventy-seven of those accounts were disabled between 64 and 351 days late, and 33 had no record of ever being disabled. BetterCloud's 2026 survey of 525 IT and security professionals found 18% of organizations had suffered a data breach in the past 12 months caused by an offboarded user who still had access.
How much does user provisioning automation cost to buy?
List prices for the lifecycle SKUs, fetched 4 September 2026: Microsoft Entra ID Governance is $7.00 per user per month paid yearly and sits on top of Entra ID P1 at $7.00, so $14 all in. Okta Workforce Identity Essentials, the tier that includes Lifecycle Management, is $17 per user per month with a $1,500 annual contract minimum. BambooHR Core is $10 per employee per month, or a monthly flat rate starting at $250 at 25 employees or fewer. Rippling publishes no per-user price at all; its pricing page routes to a quote request.
How fast should you deprovision a departing employee's accounts?
Same day, and within the hour for an involuntary departure. USAID's own policy, ADS 545, requires 24 hours, and its Inspector General found the agency missed that window on its travel system for 76% of separated users, disabling 77 accounts between 64 and 351 days late. The accounts were not dormant either: almost 57% of one sampled group, 19 of 33 users, accessed the travel system after their separation date, including eight who did so more than 325 days after leaving. Revoke first and restore afterwards if you got it wrong. Restoring takes minutes.